
Preparing Azure for application migration
The Dr. Max group runs a pharmacy network in several countries, along with e-commerce and internal applications. The decision to move operational applications to Microsoft Azure required networking, security, rules and tools that application teams can use on their own.
Since 2021 we have designed and built the Azure cloud environment for Dr. Max and helped with the gradual migration of operational applications. The collaboration started with architecture consulting and continued through several successive migration phases.
Landing zone as code
The foundation is a hub-and-spoke landing zone, described entirely in Terraform. The hub contains shared services, the firewall and DNS. Development, test and production environments are separated in their own subscriptions. Application Gateway with WAF publishes applications to the internet, and firewall rules are managed as code.
The design also covered monitoring, auditing and backup, private service connectivity and Azure Policy. We first validated the environment in a separate test tenant and only then deployed it to production.
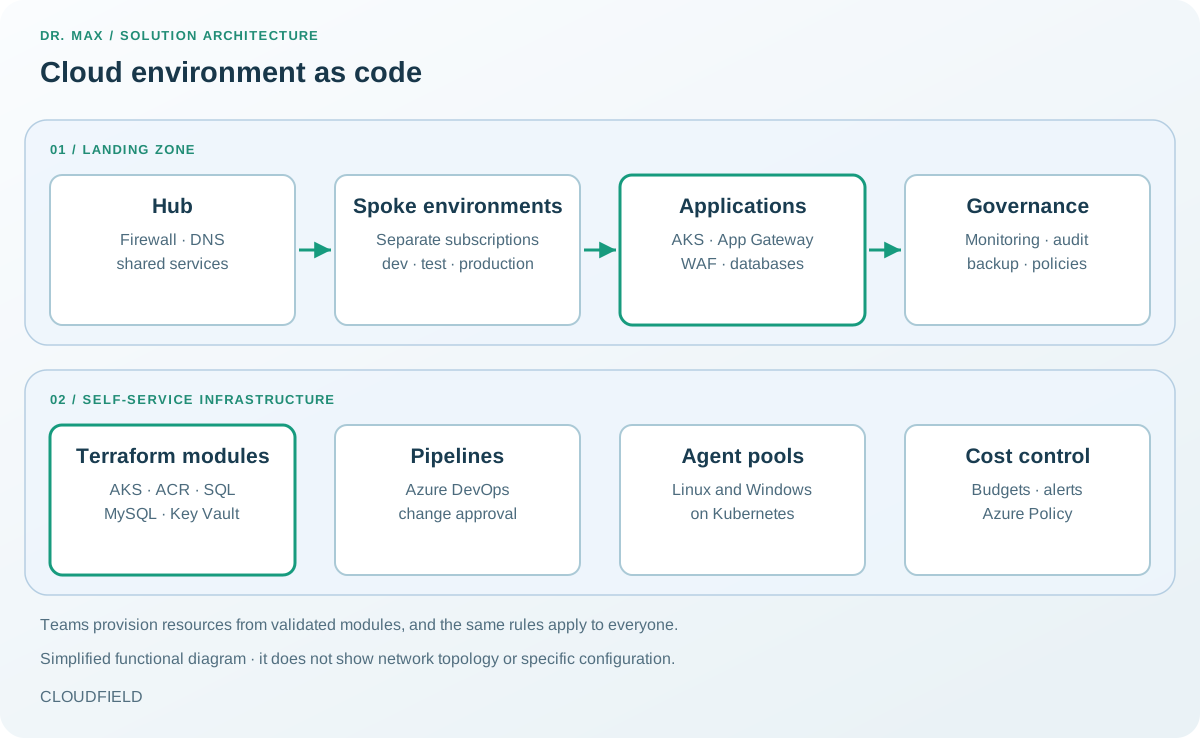
Simplified functional diagram. It does not show network topology or specific environment configuration.
Self-service infrastructure for application teams
Application migration relies on a set of validated Terraform modules. Teams use them to create AKS clusters, container registries, MSSQL, MySQL and PostgreSQL databases, Key Vault, virtual machines or Azure Functions. The modules include consistent naming, tags, identities and network integration, so every new resource follows the same rules.
Changes go through Azure DevOps pipelines with approvals between environments. Builds and deployments run on Linux and Windows agent pools hosted on Kubernetes. Module code is checked with tflint and checkov, and delivery includes documentation and handover to internal teams.
Budgets and alerts help teams track costs. Managing Azure Policy rules and DNS records as code reduces manual work.
Technologies and our role
| Area | Technologies | What we deliver |
|---|---|---|
| Landing zone | Azure, Terraform, hub and spoke | Design and deployment of network and security architecture |
| Application publishing | Application Gateway, WAF, Azure Firewall | Access rules and application publishing |
| Modules | Terraform, AKS, ACR, MSSQL, MySQL, Key Vault | Self-service modules for application teams |
| CI/CD | Azure DevOps, agent pools on Kubernetes | Pipelines with approvals and build infrastructure |
| Governance | Azure Policy, budgets, tflint, checkov | Rules, cost control and code checks |
What the collaboration delivers
Dr. Max has a cloud environment where teams can provision infrastructure themselves while following shared rules. Operational applications migrate gradually on a single foundation that can be extended and audited.
“With support from Cloudfield’s experts, we built a Microsoft Azure cloud environment and are now gradually migrating our operational applications to it with their help.”
— Tomáš Charvát, Microsoft & Datacenter Team Lead, Dr. Max