
An open-source platform for machine identity management
3Key, now OmniTrust, develops OmniTrust ILM, an open-source platform for managing the lifecycle of certificates, cryptographic keys and secrets. Organisations use it to issue and renew certificates, keep an inventory of keys across stores and create digital signatures. The platform is available under the Apache 2.0 licence and runs both in the cloud and in customer environments.
Since 2020 we have contributed to the platform core, its connectors and its signing services. Our work covers analysis, design, implementation, tests and support with merging changes into the project’s main branch.
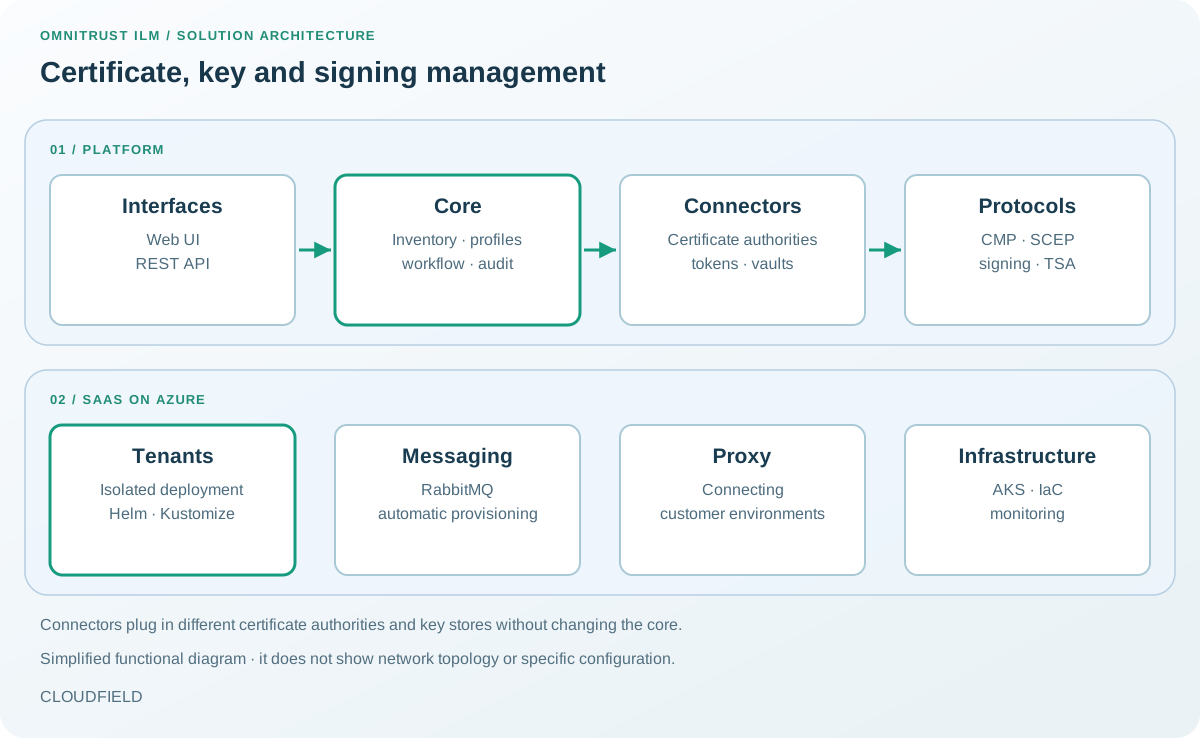
Simplified functional diagram. It does not show network topology or specific deployment configuration.
01 / The platform as SaaS on Azure
The platform was built for deployment at customer sites. So that 3Key could also offer it as a service, we prepared the analysis and carried out the transformation into a multi-tenant SaaS on Azure.
The analysis described options for provisioning, infrastructure as code and communication between the central platform and customer environments. Implementation followed: isolated tenant deployment with Helm and Kustomize, automatic RabbitMQ messaging provisioning, a proxy for connecting customer environments and core changes for multi-tenant operation. It also included support with merging the SaaS branch back into mainline development, code reviews and fixes for static-analysis findings.
02 / Signing and timestamps
Electronic signatures need securely stored keys, verifiable time and a standard interface for applications. For 3Key we developed several connected parts:
- Remote signing through the CSC API. An implementation of the Cloud Signature Consortium standard: credential management, key generation, document-hash signing, AdES signature augmentation and Keycloak authentication.
- Signing-server extensions. PAdES and XAdES signatures including visible signatures, CMS, client-side hashing, batch signing, raw and PKCS#1 signatures and long-term key pools.
- Signing in the ILM platform. A signing engine, signing profiles and signing records, a timestamping service (TSA) with time-accuracy monitoring and a PKCS#11 connector for hardware modules.
03 / Connectors, protocols and access control
We connect the platform to certificate authorities and key stores. Our work includes:
- connectors to Microsoft AD CS certificate authorities and HashiCorp Vault, cryptographic tokens for remote signing and RA profile support,
- protocols CMP and SCEP for automated certificate issuance, including support for a new cryptography provider version,
- access control at the level of individual objects and securing of platform services,
- key and token management, including token profiles, instance creation and key-management updates.
Technologies and our role
| Area | Technologies | What we deliver |
|---|---|---|
| Core and connectors | Java, Spring, REST API | Core, connector and integration-test development |
| Protocols | CMP, SCEP, CSC API | Standards for certificate issuance and signing |
| Signing | PAdES, XAdES, CMS, TSA, PKCS#11 | Signing services, timestamps and HSM integration |
| Identity and access | Keycloak, RBAC/ABAC | Authentication and object-level authorisation |
| SaaS | Azure, AKS, Helm, Kustomize, RabbitMQ | Multi-tenant deployment and operations |
What the collaboration delivers
Our work has added connectors, signing services and support for SaaS operation to the platform. We work directly with the 3Key team and merge changes into the shared open-source project.
“Cloudfield develops applications for us in security, PKI and data protection (including PCI), which we run both in our cloud and in end customers’ environments.”
— Roman Cinkais, CEO, 3Key (now OmniTrust)